

If you use AWS, Azure, and Google Cloud, the main job is simple: run the same security rules across all three. Multi-cloud can cut lock-in and help with uptime, but it also adds gaps in identity, logging, data controls, network rules, vendor review, and incident handling.
I’d sum up the article like this:
- 63% of organizations now use more than one cloud provider
- Teams often deal with 2.7 cloud environments on average
- 49% of security teams report multi-cloud problems
- Only 30% of organizations have one shared security setup
- 22% of data breaches start with credential abuse
So the article’s main point is clear: more cloud providers mean more room for drift. The fix is not more point tools. It is one security model that covers:
- IAM
- data protection
- logging and CSPM
- network segmentation
- policy and governance
- vendor risk
- incident response
The piece also ties those seven areas to native controls in AWS, Azure, and Google Cloud, then closes with a leadership checklist built around one rule: every control needs an owner, a test, and a review cadence.
| Area | What the article says to standardize | Main outcome |
|---|---|---|
| Identity | MFA, least privilege, RBAC, JIT access | Lower account misuse risk |
| Data | Encryption, key policy, masking | Same data rules in each cloud |
| Visibility | Logs, alerts, CSPM | One risk view |
| Network | Segmentation, routing, firewalls | Fewer cross-cloud gaps |
| Governance | Policy-as-code, approvals, exceptions | Same rules across providers |
| Vendors | Audit scope, SoA, partner access | Lower third-party risk |
| Response | Shared playbooks, automated actions | Faster containment |
If I were reading this as a leader, my takeaway would be: pick one cross-cloud model, assign owners, and test it every month or quarter.
AWS re:Invent 2025 – Multicloud security best practices (HMC318)
sbb-itb-2fdc177
Why Multi-Cloud Security Needs Its Own Operating Model
AWS, Azure, and Google Cloud each work in their own way. They have different control planes, different service names, and different permission models. That sounds like a tooling issue at first, but it quickly turns into a security issue.
When teams run each cloud on its own, controls often drift. One team may lock down identity in AWS, while another uses a different setup in Azure. Logging may be strong in one provider and weak in another. The result is a patchwork that’s hard to manage and even harder to trust.
That’s a big reason consistent policy enforcement breaks down in multi-cloud setups. 49% of cybersecurity professionals report difficulties across multi-cloud environments, and only 30% of organizations have unified security solutions. For many organizations, that means mismatched controls, uneven identity policies, and a blurry view of overall risk.
Leadership also runs into a plain, practical problem: separate cloud dashboards don’t give one clear picture. If exposure sits in three different places, decision-making gets messy fast. A unified operating model gives teams a single control plane – one place to manage policies, track posture, and respond to incidents across every provider. Without that, leaders lose a direct view of exposure, priorities, and response.
Identity should come first. It’s the control most teams need to standardize before anything else. From there, the model extends across the rest of the stack:
- identity
- data protection
- logging
- network controls
- governance
- vendor oversight
- incident response
These seven practices define the operating model.
1. Unified Identity and Access Management
Start by standardizing identity across AWS, Azure, and Google Cloud. Every user and service account adds risk, and credential abuse is the starting point for 22% of all data breaches. This first layer makes later policy, logging, and response work much easier to apply across clouds.
The goal is simple: move away from standing access and toward Just-In-Time (JIT) access. That means access is granted for a limited time, logged, and then removed when the job is done. It sounds small, but it changes the day-to-day security picture in a big way.
To make that work, teams need a clear view of permissions across providers. Cloud Infrastructure Entitlement Management (CIEM) helps by showing who can access what across all clouds, making it easier to spot overprivileged accounts and missing entitlements. A unified IAM model also supports audit-ready access records through continuous monitoring and documented remediation workflows.
Standardize these four controls first:
| Control | Governance Value |
|---|---|
| MFA | Needed for all administrative access across providers |
| Least-Privilege | Limits blast radius if one account is compromised |
| RBAC | Creates repeatable, auditable access patterns |
| Automated Provisioning | Helps prevent orphaned accounts and shadow IT across providers |
Once identity is locked down, the next step is consistent data protection and key control.
2. Consistent Data Protection and Key Management
After identity, the next step is to standardize encryption, data handling, and key control across AWS, Azure, and Google Cloud. When each cloud uses different tools and workflows, encryption settings and access controls start to drift. That’s when gaps show up. The fix is simple in principle: set one encryption and key policy for every cloud.
Use ISO 27001, ISO 27017, and ISO 27018 as the shared control baseline across clouds. ISO 27018 is especially useful for standardizing PII protection across providers. Then map those standards to day-to-day controls like key ownership, data masking, and access reviews.
Real-time data masking and data access controls can limit unauthorized access. Automated compliance monitoring also helps teams stay audit-ready. Instead of managing separate rules for each provider, use one policy for encryption, masking, and key access across all three clouds. JIT workflows cut standing access to encryption keys.
Once data and keys are standardized, logging and monitoring become much easier to enforce.
3. Centralized Logging, Monitoring, and CSPM
AWS, Azure, and Google Cloud each produce their own logs and alerts. If you leave that data scattered, teams lose a single view of risk. For executives, that means dealing with one comparable risk view across AWS, Azure, and Google Cloud instead of three mismatched reports. The aim is simple: fast detection, clear ownership, and one remediation path across all clouds.
When monitoring isn’t centralized, policy drift can sit in the background until it turns into an incident. That’s why centralized logging and CSPM matter. CSPM pulls logs and alerts from every cloud into one place, giving teams one alerting and remediation path no matter where the issue lives. Fragmented tools do the opposite. They lead to uneven enforcement and slower response.
Focus on the signals that matter most:
- identity activity
- configuration drift
- compliance logs
Real-time alerts help leaders check critical events right away.
CSPM should also tie each finding to a clear remediation step. That cuts alert fatigue and helps security teams stay focused on what matters most. For executives, this again means one comparable risk view across AWS, Azure, and Google Cloud.
With visibility centralized, the next move is to standardize network segmentation and connectivity across clouds.
4. Standardized Network Segmentation and Connectivity
Once visibility is in one place, the next move is to standardize how traffic flows between clouds.
Set the same segmentation and connectivity baseline across AWS, Azure, and Google Cloud. That means one control model for routes, firewalls, private links, and access rules. From there, apply least-privilege network access by default, lock down east-west and north-south traffic, and use continuous drift detection with auto-remediation when someone makes an unauthorized change. The goal is simple: give security teams one network model they can enforce, not three separate ones.
This matters because misconfigurations often slip in through small differences between cloud setups. One team handles routing one way in AWS, another sets firewall rules a bit differently in Azure, and before long, the picture gets messy. Using the same firewall rules, routing policies, and private connectivity standards in every environment cuts that risk down fast.
It also helps to limit privileged network changes to JIT approval. That way, unauthorized modifications are less likely to stick around unnoticed.
Standardized segmentation also makes audits less painful. When each environment follows the same control model, security teams can track policy adherence across providers without trying to reconcile three different rule sets. And once network boundaries are consistent, governance can enforce those boundaries across all providers.
5. Cross-Cloud Security Policy and Governance
Once network controls are standardized, governance answers the next set of questions: who can change them, how exceptions get approved, and how compliance gets tracked. In a multi-cloud setup, that means turning shared network standards into rules that can be enforced across AWS, Azure, and Google Cloud. Put simply, governance applies the same guardrails to the network baseline set in the previous section.
Use ISO 27001 as the governance baseline, then map each provider’s controls to ISO 27017 and ISO 27018. All three major cloud providers are certified under ISO 27001, which gives security teams a common framework for risk management and control documentation. ISO 27017 and ISO 27018 build on that base with cloud-focused controls and PII protection.
Governance also needs to go beyond passing audits. A clean audit is nice, but it only shows a snapshot in time. What leaders need is proof that controls are working day to day. That’s where policy-as-code, approval workflows, and exception tracking come in. They help keep controls aligned across clouds instead of letting each platform drift in its own direction. For privileged policy changes, apply just-in-time approval so high-risk actions get tighter review.
For leadership teams, the clearest proof usually comes from audit reports, exception logs, and policy-attestation records. Those records show that the security posture is being managed actively, not checked once in a while. With policy ownership in place, the next step is figuring out which cloud vendors and services bring the most exposure.
6. Cloud Vendor Risk Management
Governance sets the rules. Vendor risk management checks whether cloud providers, and the companies behind them, can actually meet those rules.
The big three cloud providers all hold independent third-party audit certifications. That helps, but it doesn’t settle the issue. Leaders still need to verify the audit scope, the services covered, and the controls that were tested.
Audit scope matters just as much as the certificate itself. Azure, for example, includes 61 customer-facing services within its ISO 27001 and ISO 27018 audit scope, which can reduce how much internal review work your team needs to do. But that only tells part of the story. You still need to check which controls were tested.
Don’t stop at the certificate. Ask each provider for its Statement of Applicability (SoA) so you can confirm exactly which controls and services were in scope.
That review should also go beyond the cloud provider alone. Look at fourth-party dependencies and service integrations too. This is where things can get messy fast. Third-party involvement in data breaches doubled from 15% to 30% in a single year, and the average supply chain compromise cost reached $4.91 million.
Use time-bound access for third-party partners. Standing vendor access leaves the door open longer than it should. A better approach is temporary, logged access workflows, which can reduce blast radius if a vendor account is compromised. The same discipline should carry into incident response planning.
7. Multi-Cloud Incident Response Playbooks
Incident response is where centralized controls have to do the work. In a multi-cloud setup, AWS, Azure, and Google Cloud may need the same containment standard, but the steps to get there are different. That’s why a playbook matters. It spells out who does what the moment an incident starts, with cloud-native actions for each provider. The main point is speed: the first few minutes should be scripted, not made up on the fly.
Without a single playbook, teams tend to improvise under pressure. That slows containment and gives the issue more room to spread.
Use the same security platform that powers monitoring and alerts to kick off response actions across all clouds. As soon as alerts fire, the playbook should move straight into containment. Automate steps like:
- closing ports
- revoking excess access
- isolating compromised workloads
It also helps to pair those actions with Just-in-Time (JIT) access during containment. That can cut down the spread of credential-based compromise.
Use ISO 27001 to set response roles, escalation paths, evidence collection, and post-incident review across providers. This keeps escalation and evidence handling consistent across AWS, Azure, and Google Cloud.
The control mapping below shows how these response steps line up across the three clouds.
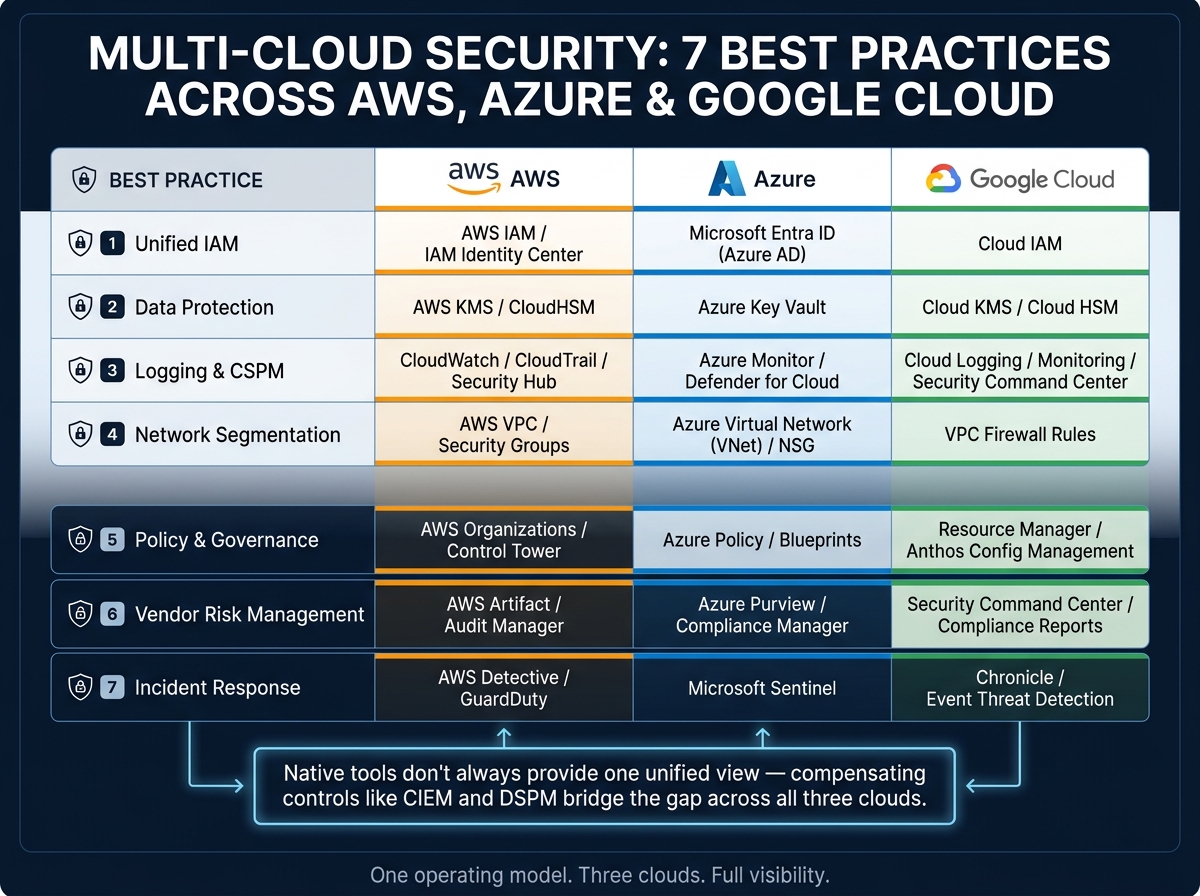
AWS, Azure, and Google Cloud Control Mapping at a Glance
Multi-Cloud Security: 7 Best Practices Across AWS, Azure & Google Cloud
Each of the seven practices lines up with native controls in AWS, Azure, and Google Cloud. The hard part isn’t finding the tools. It’s making sure those controls stay visible and governed across every cloud you use.
Use the table below to translate the seven practices into the native controls tied to each platform. Then match each practice to the control your team owns in each cloud.
| Best Practice | AWS | Azure | Google Cloud |
|---|---|---|---|
| 1. Unified IAM | AWS IAM / IAM Identity Center | Microsoft Entra ID (Azure AD) | Cloud IAM |
| 2. Data Protection | AWS KMS / CloudHSM | Azure Key Vault | Cloud KMS / Cloud HSM |
| 3. Logging & CSPM | CloudWatch / CloudTrail / Security Hub | Azure Monitor / Defender for Cloud | Cloud Logging / Monitoring / Security Command Center |
| 4. Network Segmentation | AWS VPC / Security Groups | Azure Virtual Network (VNet) / NSG | VPC Firewall Rules |
| 5. Policy & Governance | AWS Organizations / Control Tower | Azure Policy / Blueprints | Resource Manager / Anthos Config Management |
| 6. Vendor Risk Management | AWS Artifact / Audit Manager | Azure Purview / Compliance Manager | Security Command Center / Compliance Reports |
| 7. Incident Response | AWS Detective / GuardDuty | Microsoft Sentinel | Chronicle / Event Threat Detection |
Native tools don’t always give you one clear view across all three providers. That’s where compensating controls like Cloud Infrastructure Entitlement Management (CIEM) and Data Security Posture Management (DSPM) come in. They help teams see user permissions and data exposure across AWS, Azure, and Google Cloud in one place, which supports the single operating model this article is built around.
Assign one owner for each control in each cloud. Then use that ownership map in the checklist below.
Multi-Cloud Security Governance Checklist for Leaders
Ownership without verification is just paperwork.
This checklist gives CEOs, CIOs, and CISOs a fast way to confirm controls are active, not merely written down. Use the control map above to turn each native control into an executive check that can be reviewed on a set cadence. Each row below ties the work to an owner, a test, and a review schedule.
| Control Area | Leadership Verification Action | Accountability Owner | Review Cadence |
|---|---|---|---|
| Phishing-Resistant MFA | Confirm phishing-resistant MFA is enforced for all admin accounts across AWS, Azure, and Google Cloud. | CISO | Monthly |
| Least-Privilege Role Design | Use CIEM reports to find and fix overprivileged accounts. Confirm JIT workflows have replaced standing access. | IAM Lead | Monthly |
| Customer-Managed Key Policies | Validate key rotation schedules and approved key policies for regulated data. | Data Security Lead | Monthly |
| Centralized Audit Logging | Test real-time alerting with a controlled root-account password change. Measure how fast leadership is notified. | Security Operations Lead | Monthly |
| Cross-Cloud Policy Baselines | Review CSPM drift reports for policy deviations across AWS, Azure, and Google Cloud. | Cloud Governance Lead | Monthly |
| Segmented Network Architecture | Verify network segmentation across cloud environments. Confirm there is no unneeded flat access. | Network Security Lead | Monthly |
| Documented Vendor Reviews | Confirm current ISO 27001, ISO 27017, and ISO 27018 certifications for each provider. | Vendor Risk Lead | Quarterly |
| Tested Incident Response Drills | Test playbooks for a cross-cloud breach scenario. Document gaps and remediation timelines. | CISO / IR Lead | Quarterly |
A checklist like this does two things at once. It shows who owns each control, and it makes the review concrete enough that leadership can ask, “Was this tested?” instead of “Do we have a policy for it?”
That shift matters. A monthly check on MFA, logging, and access design can expose drift before it turns into a bad headline. Quarterly reviews on vendors and incident drills help keep outside risk and response readiness from slipping through the cracks.
Conclusion
Multi-cloud security comes down to using the same controls across AWS, Azure, and Google Cloud. More tools won’t fix the problem. One operating model will.
The seven practices – unified IAM, data protection, centralized logging, network segmentation, cross-cloud governance, vendor risk management, and incident response – help cut misconfiguration risk and make it easier to see what’s happening. Standards like ISO 27001 also give teams a shared way to manage security across cloud providers.
But a framework on paper isn’t enough. It only works when leadership assigns clear ownership and reviews controls on a set cadence. For CEOs, CIOs, and CISOs, the real sign of progress isn’t whether a policy document exists – it’s whether controls are active, tested, and owned. The checklist above turns that into something plain to verify: every control needs an owner, a test, and a cadence.
FAQs
Where should we start with multi-cloud security?
Start with a clear strategy that connects security goals to your organization’s risk appetite and business goals.
Focus first on your most critical data and assets, where they live, and who owns them across leadership, IT, security, and compliance. From there, put the top safeguards in place, especially identity and access management and continuous monitoring.
How do we enforce the same policies across AWS, Azure, and Google Cloud?
Centralize governance so teams follow the same rules and enforcement doesn’t turn into a guessing game. Set one shared standard for least privilege, encryption, logging, DLP, network micro-segmentation, and phishing-resistant MFA. Then track those controls with one consistent monitoring and metrics approach across teams and cloud accounts.
Policies shouldn’t sit still. As access patterns, data handling, and risk thresholds shift, update them on a regular basis. It also helps to test response playbooks and escalation rules across all environments, so people know what happens, who steps in, and where things can break before an incident puts that to the test.
How often should leaders review multi-cloud security controls?
Leaders should review multi-cloud security controls at least quarterly so the work lines up with board oversight and reporting cycles.
For critical systems or higher-risk setups, use continuous automated monitoring and move reviews to monthly while active projects are in progress.
Any major change, major incident, or newly discovered vulnerability should trigger immediate updates to the related controls and policies.