

A vendor can hit every SLA and still put you at risk. That’s the main point.
If I had to sum up the article in a few lines, I’d say this:
- KPIs show delivery
- KRIs show exposure
- KPIs look back at what happened
- KRIs point to what may go wrong next
- You need both in the same vendor report
That matters because a vendor can post 99.9% uptime and still have a growing list of security gaps, audit issues, or money problems. And the risk is not small: 61% of companies said they had a third-party breach or cyber incident in 2023, up 49% year over year.
If I’m reviewing a vendor report, I want two things side by side:
- Performance results like on-time delivery, uptime, defect rate, and cost per transaction
- Risk signals like cyber incidents, audit findings, turnover in key roles, financial stress, and concentration risk
The article’s core idea is simple: don’t blend service results and risk into one fuzzy status update. Keep them separate, show them together, and use that view to decide whether to maintain, remediate, escalate, or exit.
Quick comparison:
| Area | KPI | KRI |
|---|---|---|
| What it shows | Service delivery | Risk exposure |
| Time view | Past results | Near-term warning signs |
| Common examples | Uptime, SLA hits, defect rate, cost | Security findings, credit issues, audit items |
| Main use | Track vendor performance | Spot risk drift |
| Common action | Service fixes, SLA follow-up | Mitigation, watchlist, escalation |
So if you want a vendor report that helps you make decisions, not just log data, the formula is pretty clear: put KPI scorecards first, KRI thresholds next, then show exceptions, owners, due dates, and the final decision.
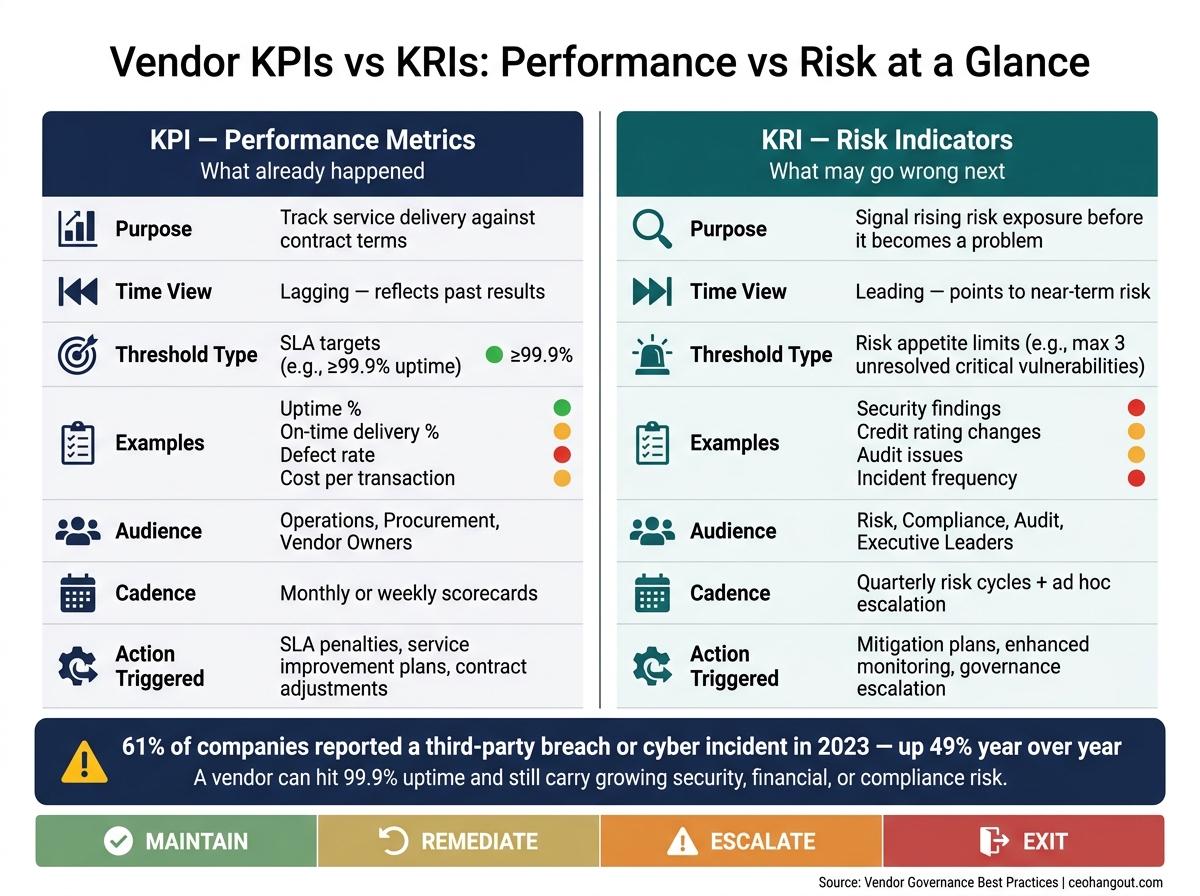
Vendor KPIs vs KRIs: Performance vs Risk at a Glance
The Right KRIs and KPIs for Measuring Third-Party Risk
sbb-itb-2fdc177
Vendor KPIs: What Performance Metrics Measure
On the performance side, vendor reports use KPIs to show whether the vendor delivered on work, quality, and cost terms in the last reporting period.
Vendor KPIs are backward-looking metrics. They show whether a vendor met its contract terms during the last reporting period, which is usually a month or a quarter. That matters because KPIs give teams a record they can compare over time for sourcing, renewals, and escalation decisions.
Common KPI Categories in Vendor Scorecards
Vendor scorecards usually group KPIs into five main areas: service delivery, efficiency, quality, contract compliance, and business outcomes. Most teams keep scorecards tight, with 5–8 KPIs per vendor.
These are the categories executives tend to scan first:
| KPI Category | Example Metrics | Typical Benchmark |
|---|---|---|
| Service Delivery | On-time delivery rate, OTIF, service uptime, lead time | ≥95–98% on-time delivery; ≥93–95% OTIF; 99.9% uptime for critical systems |
| Efficiency | Procurement cycle time, average ticket handling time, output per employee | Tracked against the baseline or prior period |
| Quality | Defect rate, return rate, error rate, MTTR, first-contact resolution | <1% defect rate; MTTR under 4 hours for P1 incidents; first-contact resolution ≥80–85% |
| Contract Compliance | SLA compliance rate, contract fulfillment rate, invoice accuracy | ≥95–98% contract compliance rate; ≥98% invoice accuracy |
| Business Outcomes | Cost savings achieved vs. baseline, ROI, revenue enabled | Measured against the agreed baseline and often shown in USD |
How KPIs Appear in Reports
A solid KPI scorecard gives leaders a fast executive read. Most reports use a target-vs.-actual layout, like "Uptime target: 99.9% | Actual: 99.7%", so misses stand out right away.
Each metric also gets a red-amber-green status. Green means the vendor hit target. Amber points to a small miss. Red signals a major or repeated breach.
Reports often include trend lines or sparklines to show month-over-month or quarter-over-quarter movement. That way, leaders can see if performance is getting better or slipping.
Quarterly reports often add a composite vendor score based on weighted KPIs across delivery, quality, cost, and compliance. Executives use that view to confirm service performance before they move to risk exposure.
That covers the performance side of the report. The next section turns to the risk side.
Vendor KRIs: What Risk Indicators Measure
KRIs are forward-looking signals that show rising exposure, even when service levels still look green. That matters because a vendor can hit service targets while, behind the scenes, security, compliance, or financial pressure keeps building.
In practice, KRIs help with ongoing monitoring for critical or material vendors. They give risk teams an early heads-up before a problem turns into a bigger issue. The next section looks at those risk signals next to performance results so you can see both at once.
Common KRI Categories in Vendor Oversight
These are the signals leaders watch when performance alone seems fine. Teams use them to spot triggers for a watchlist, escalation, or remediation.
| KRI Category | What It Tracks | Example Warning Signal |
|---|---|---|
| Operational Risk | Incident frequency, slow incident resolution, change management/control exceptions, and capacity or availability risks | Repeated major incidents or incident backlog triggers escalation |
| Cyber & Security | Unresolved high-severity vulnerabilities, open security audit findings, patch cadence, and security incidents or near-misses | A buildup of critical findings or control gaps triggers red status |
| Financial Health | Credit rating changes, internal financial risk scores, key ratio deterioration, and going-concern warnings | A falling financial score or adverse credit event prompts a watchlist review |
| Regulatory & Compliance | Missed attestations, compliance breaches, audit findings, and overdue regulatory reporting | Missed filings or unresolved compliance items are escalated |
| Concentration & Dependency | Reliance on a single vendor, subcontractor exposure, and fourth-party risk | Too much critical work concentrated in one provider triggers executive review |
Subcontractor and fourth-party exposure need extra scrutiny. Hidden dependencies can create risk that normal performance metrics never show. A vendor may look fine on paper, but if key work sits with downstream providers you can’t clearly see, that’s a problem. Risk teams often review how much visibility they have into those providers and treat limited visibility as a warning sign on its own.
How KRIs Appear in Reports
KRI dashboards are built around thresholds, not averages. Most reports use green, amber, and red markers to show how close a vendor is to a risk boundary. In plain English, thresholds show when a vendor is getting close to escalation.
Trend arrows, sparklines, and aging metrics add context. They show whether a KRI is improving, stable, or getting worse, and how long an open risk item has stayed unresolved. For critical vendors, reports usually add a short narrative that explains the root cause of an exception and the remediation plan, not just a color code. That makes side-by-side comparison with KPI results much easier in the next section.
KPI vs. KRI: What Performance Reports Show Side by Side
The table below shows how vendor reports split service performance from risk exposure.
Comparison Table: KPI vs. KRI in Vendor Reporting
| Aspect | KPI (Performance) | KRI (Risk) |
|---|---|---|
| Purpose | Show whether the vendor met agreed service levels | Show whether the vendor relationship is becoming riskier |
| Measurement focus | Uptime %, on-time delivery %, cost per transaction (USD), ticket resolution time | Unresolved security findings, credit rating changes, regulatory audit issues, incident frequency |
| Time orientation | Lagging – reflects what already happened | Leading – signals what may happen next |
| Threshold type | SLA targets (e.g., ≥99.9% uptime) | Risk appetite limits (e.g., no more than 3 unresolved high-severity vulnerabilities at any time) |
| Typical audience | Operations managers, procurement, vendor owners | Risk, compliance, audit, and executive leaders |
| Reporting cadence | Monthly or weekly scorecards | Quarterly risk committee cycles, with ad hoc escalation on threshold breaches |
| Action triggered | Service improvement plans, SLA penalties, contract adjustments | Risk mitigation plans, enhanced monitoring, contingency planning, governance escalation |
Put simply, KPIs track service delivery and KRIs track risk drift.
KPIs belong in management dashboards. KRIs belong in governance reports. In practice, both need to sit next to each other in executive vendor reviews. If you only look at one side, you can miss the story that matters.
Why Strong KPIs Can Coexist With Weak KRIs
This is where things get tricky. A vendor can look great on paper from a service standpoint while risk keeps creeping up in the background.
Take a hypothetical but realistic example. A U.S.-based cloud services vendor posts 99.98% uptime and hits every SLA response-time target. The operations team sees a green KPI scorecard across the board. So far, so good.
But then the KRI panel shows something else. Over three months, unresolved critical security findings from penetration tests go from 2 to 10. Average time to patch high-severity vulnerabilities jumps from 7 days to 30 days. Several minor unauthorized access attempts are logged and contained, but the pattern suggests security risk is getting worse.
The service looks fine. The risk does not.
You see the same issue in other cases too. Delivery can stay strong while financial stress builds, or while compliance problems start piling up. That’s why side-by-side reporting matters so much. It helps leaders answer the real review question: keep the vendor as is, tighten controls, or escalate.
How Leaders Use Both Metrics in Vendor Reviews and Decisions
After comparing KPIs and KRIs side by side, leaders use that combined view to decide what happens next. Executives want a simple answer: what do these two sets of metrics show together, and what action should follow?
In most cases, the answer falls into one of four paths: maintain, remediate, escalate, or exit.
That choice depends a lot on how the report is arranged.
A Balanced Report Layout for Executive Review
A strong vendor review pack should move in a clear, logical order.
Start with the KPI scorecard. This gives leaders a quick read on service delivery, usually with traffic-light status and trend arrows. Right after that, show the KRI dashboard, which brings risk signals to the surface with clear thresholds and trend direction.
Then comes the proof behind the decision: the exceptions and remediation section. This part should spell out the issue, impact, severity, owner, and due date. After that, decision notes should record the final call, the reason for it, and any residual risk.
For critical vendors – those that support core revenue, regulated processes, or key operations – KRI escalation thresholds should be lower, and response timelines should be shorter. A drop in a security score or an overdue compliance assessment might be manageable for a lower-tier vendor. But for a critical vendor, that same issue can call for immediate senior attention.
Grouping vendors by tier in the report helps leaders keep their focus where performance and risk meet.
Once the report shows performance, risk, and remediation together, the executive decision is much easier to see.
Conclusion: Reading Vendor Health Clearly
KPIs alone don’t tell the whole story. KRIs alone don’t either.
The point of a balanced vendor review pack is to show both at the same time, so leaders can act on evidence instead of assumption. For executives who want to refine vendor governance practices, CEO Hangout offers peer exchange and leadership resources tied to that work.
FAQs
Can a vendor have strong KPIs but still be high risk?
Yes. A vendor can post strong KPIs for delivery speed, quality, or SLA compliance and still create serious risk.
The reason is simple: KPIs track operational performance. They show how well the vendor is doing the work day to day. But they can miss problems sitting under the surface, like security gaps, financial trouble, or regulatory non-compliance.
That’s where KRIs come in. They help leaders catch warning signs early, before those issues turn into bigger problems.
How often should vendor KPIs and KRIs be reviewed?
Review vendor KPIs and KRIs with a mix of continuous monitoring and scheduled assessments. A lot of teams rely on quarterly reviews to keep metrics tied to business goals, while automated oversight helps flag issues in real time.
Critical risks usually need review at least every quarter. General risk assessments should happen no less than twice a year. To keep these metrics useful, make reviews part of normal operations so they stay in step as priorities or threats shift.
What should trigger a vendor escalation or exit?
A vendor escalation or exit should start when performance metrics fall below set thresholds and fix attempts aren’t working.
Leaders need to step in when risk scores drop under target benchmarks, incident patterns stay unresolved, or SLA compliance, response times, or security posture keep missing expectations. At that point, it makes sense to activate contractual exit strategies and termination checklists so the transition is smooth and controlled.